Ghostscript Flaws Let Hackers Hijack Servers via PDF Uploads
Three dangerous vulnerabilities in Ghostscript now put millions of servers at risk. Attackers can exploit these flaws by uploading a malicious PDF or PostScript file to any web service that uses Ghostscript for document processing. A public proof-of-concept exploit already exists for one of them.
The most severe flaw, CVE-2026-39919, scores a critical 9.3 on the CVSS v4 scale. This heap buffer overflow sits in Ghostscript’s JPEG 2000 output adapter. When a server processes a crafted PDF with mismatched image subsampling values, the flaw corrupts chunk-allocator metadata. As a result, attackers can achieve remote code execution without any authentication.
The second flaw, CVE-2026-101258, carries a CVSS score of 8.5. This one lets attackers bypass Ghostscript’s -dSAFER sandbox entirely. The exploit chains a type 5 shading out-of-bounds write with a use-after-free of a procedure stream. Once the sandbox falls, attackers can run shell commands directly on the server. Security researchers at v12-security have already published a proof-of-concept exploit on GitHub for this vulnerability.
A third flaw also demands attention. CVE-2026-103226 targets the Pdfwrite component through a stack-based buffer overflow in the type1_callsubr function. According to Debian’s security tracker, a public exploit for this flaw already exists and “might be used.”
The real danger extends far beyond Ghostscript itself. Major platforms like Wikipedia, Steam, Microsoft OneDrive, and Mozilla’s Pocket service all use Ghostscript through ImageMagick for image processing. Furthermore, ImageMagick identifies files by their content rather than their extension. So an attacker can rename a malicious PostScript file as a .jpg image, and ImageMagick will still send it to Ghostscript for processing.
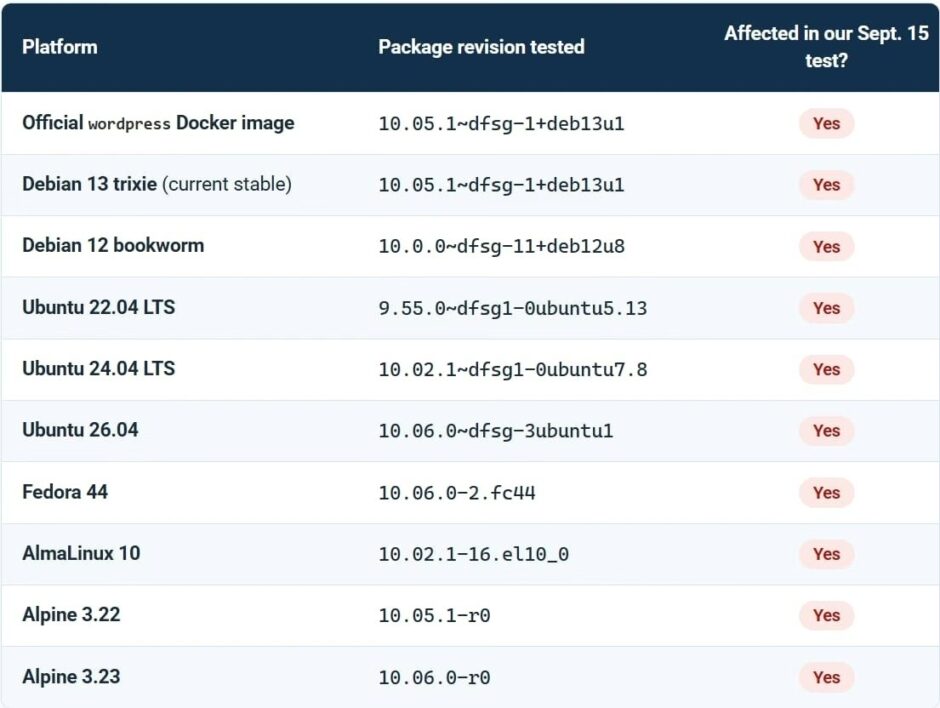
All three flaws receive patches in Ghostscript version 10.08.0. Red Hat has already shipped fixes for RHEL 8, 9, and 10 between October 1 and October 6. SUSE also released an advisory on October 8 rating CVE-2026-39919 as “important.” However, Debian Bookworm and several Amazon Linux releases still show pending fixes.
A related flaw, CVE-2026-108693, also affects ImageMagick on Windows specifically. This vulnerability lets attackers plant a malicious Ghostscript executable that runs with ImageMagick’s privileges during PDF conversion.
Server administrators should update Ghostscript to version 10.08.0 immediately. Additionally, teams should sandbox any service that processes untrusted documents and disable PostScript handling in ImageMagick’s policy.xml where possible.