Apple Releases iOS 27.2.1 With Fixes for Several Serious Security Flaws
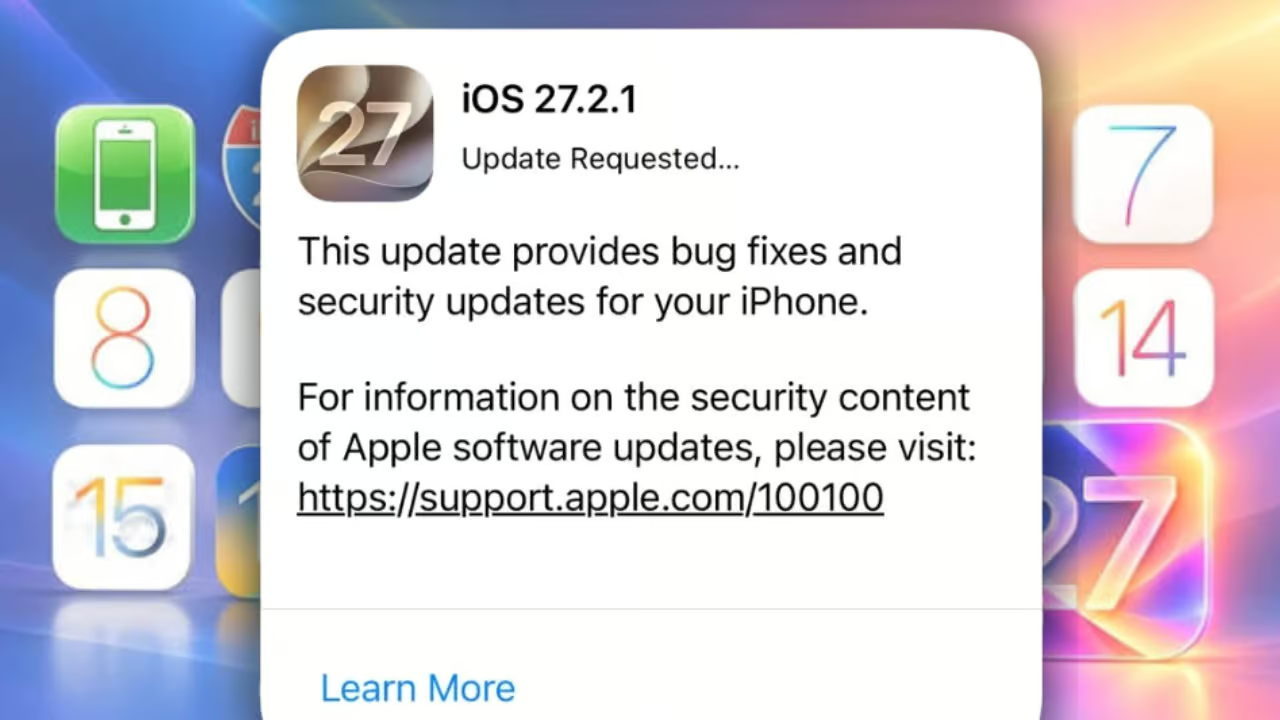
Apple released iOS 27.2.1, iPadOS 27.2.1 and macOS 27.2.1 on Monday with fixes for a number of security vulnerabilities. The updates address problems in iMessage, AirPlay and Bluetooth, along with a certificate issue that affected developer tools on Mac.
iMessage Flaws Weakened Group Chat Privacy
The most concerning issues involve iMessage. One bug could let a remote attacker join a group chat and receive its messages. Another could let users see messages that were sent before they joined a group conversation. Together, the two flaws undermined the privacy that people expect from group messaging on Apple devices.
Bluetooth and AirPlay Vulnerabilities
Most of the remaining flaws relate to Bluetooth and AirPlay. One Bluetooth bug allowed a malicious device to pair with an iPhone or iPad without any action from the user. Another let a nearby attacker corrupt process memory on the target device.
Several AirPlay vulnerabilities let attackers bypass the rate limit on pairing code attempts. This meant an attacker could guess AirPlay pairing codes repeatedly without the throttling that normally prevents rapid guessing.
Apple found four of the vulnerabilities internally, which suggests its own security team caught them before outside researchers did. The company did not say whether any of the flaws were exploited in the wild. However, now that the details are public through Apple’s security content pages, devices that have not been updated face a higher risk of targeted attacks.
macOS Update Closes eMudhra Certificate Gap
The macOS 27.2.1 update also includes a fix that developers and system administrators have been waiting for. It addresses the eMudhra certificate problem in command line tools.
In October, security researchers found that the private keys of eight intermediate certificate authorities run by the Indian company eMudhra had been compromised. Anyone holding those keys could forge valid HTTPS certificates for any website.
Apple blocked the compromised certificates in Safari, Mail and apps that use its networking frameworks on October 19. But command line tools such as Git, curl, Python 3, Ruby, Perl and OpenSSL kept accepting them. These tools check certificates against a separate file that does not consult Apple’s block list or revocation status. As a result, the macOS 27.2 update released on October 26 still left the gap open. Developers who used Git to pull code or curl to download packages remained exposed to possible man in the middle attacks. macOS 27.2.1 now adds protections for command line tools and closes the gap.
How to Update
Apple recommends updating all devices as soon as possible. On iPhone and iPad, go to Settings, then General, then Software Update. On Mac, open System Settings, then General, then Software Update.